Insights & Guidance
Blog
Practical guidance on security governance, compliance, and risk management — written for the people who actually do the work.
The Best vCISO Platforms in 2026: 7 Tools Compared for Practice Operators
Seven vCISO platforms compared through the lens that matters: can you run twenty client programs on it without the busywork scaling faster than the revenue? Criteria, honest tradeoffs, and where each tool actually fits.
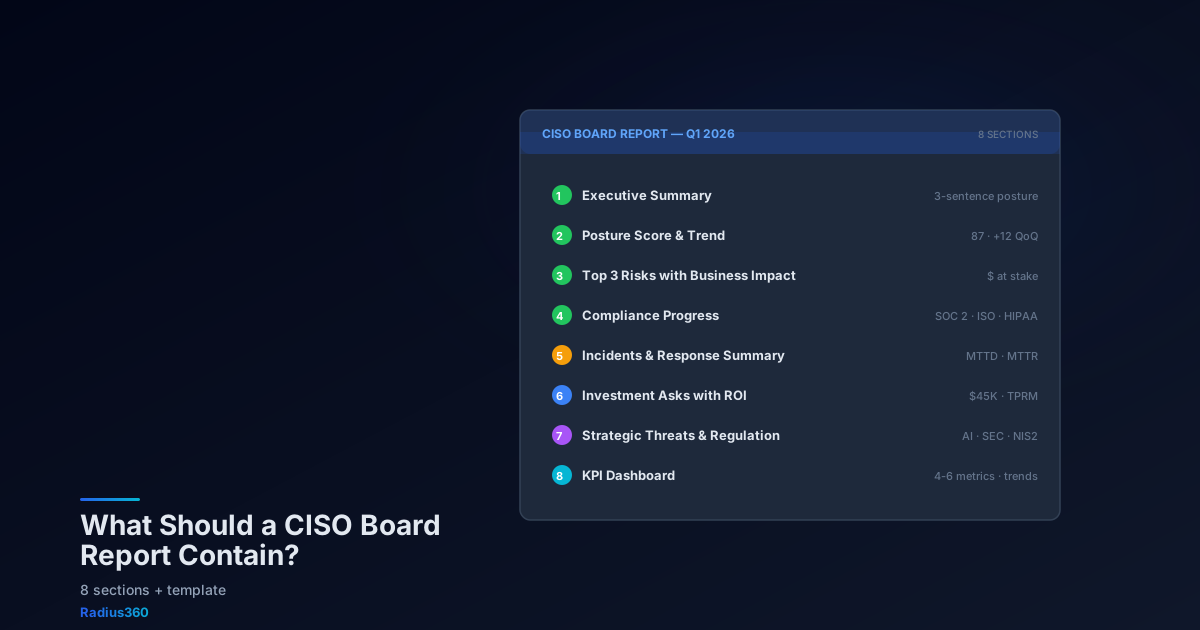
What Should a CISO Board Report Contain? 8 Sections That Actually Move the Needle
A CISO board report that actually earns approval for the budget ask: the eight sections boards want, what to put in each, and the one-page template that compresses a two-hour briefing into a 15-minute decision.
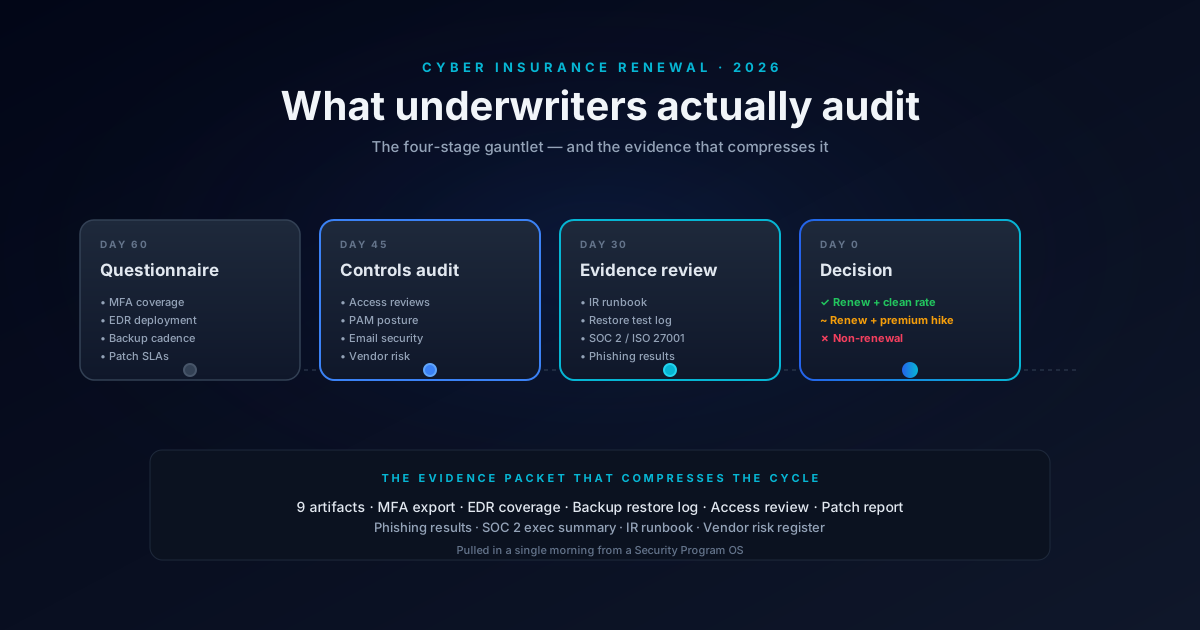
Cyber Insurance Renewal 2026: What Underwriters Actually Audit
The 2026 cyber insurance renewal decoded — what underwriters audit, the evidence packet that shortens the cycle, what triggers premium hikes, and the 60-day prep sequence that works.
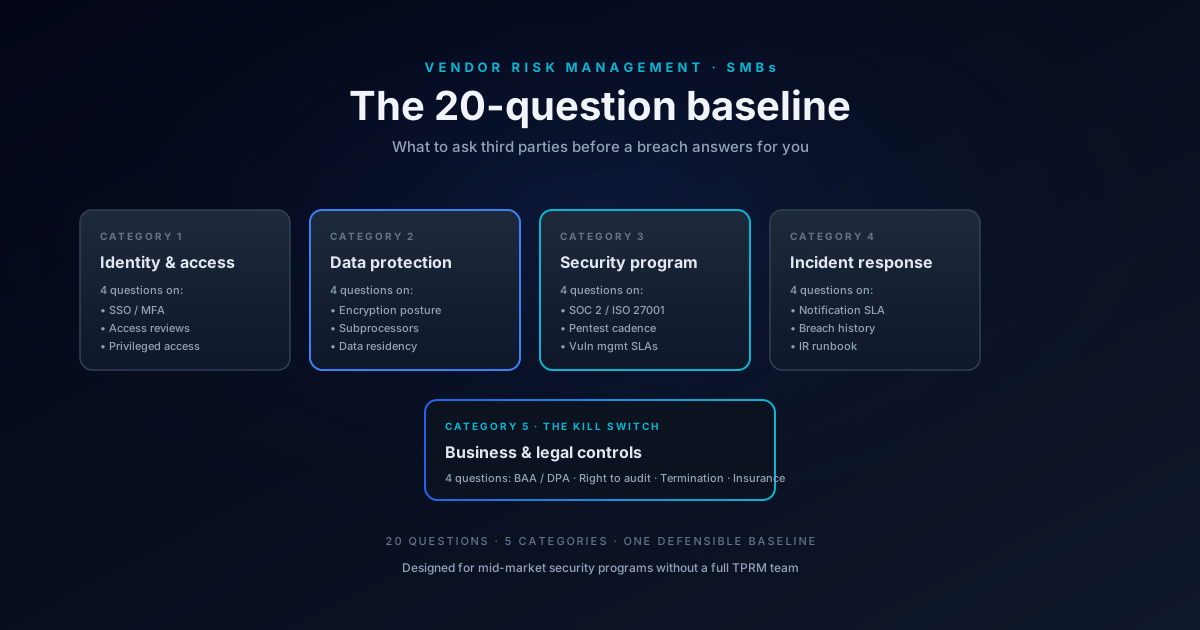
Vendor Risk Management for SMBs: The 20-Question Baseline
A practical vendor risk management baseline for SMBs — 20 questions across 5 categories that surface real risk without the enterprise-TPRM apparatus. The minimum viable program that still satisfies auditors and insurers.
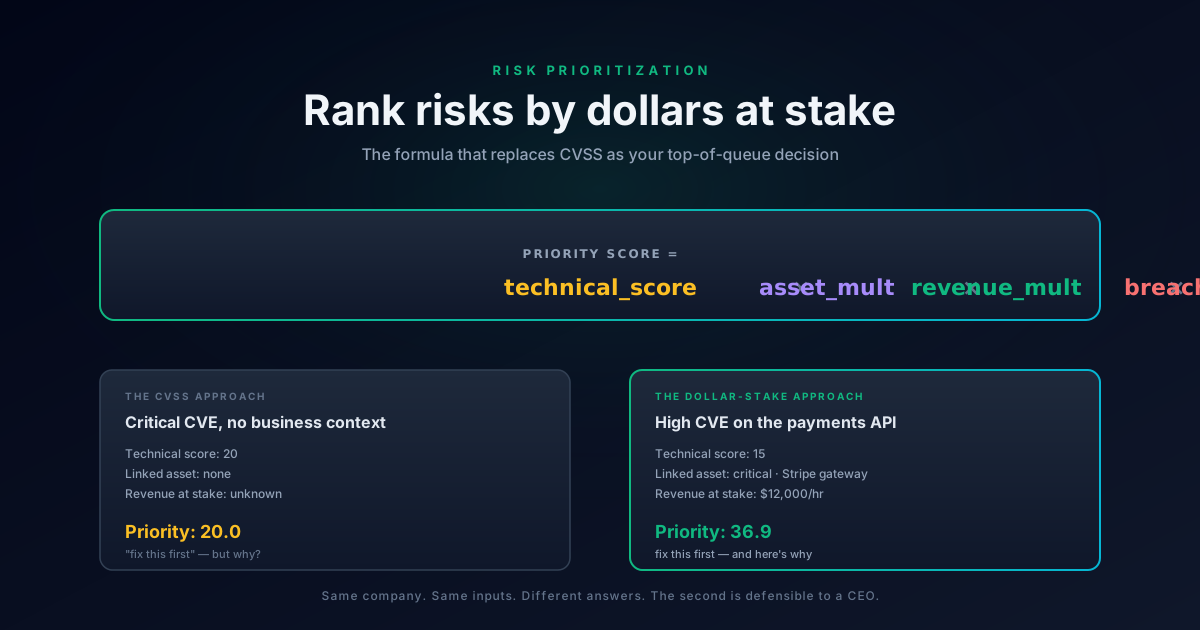
How We Rank Risks: Dollars at Stake, Not CVSS
CVSS ranks risks by how loud the scanner is. A real CISO decision-engine ranks by how much business value is at stake. Here's the formula we use and why it changes which risk ends up at the top of the queue.
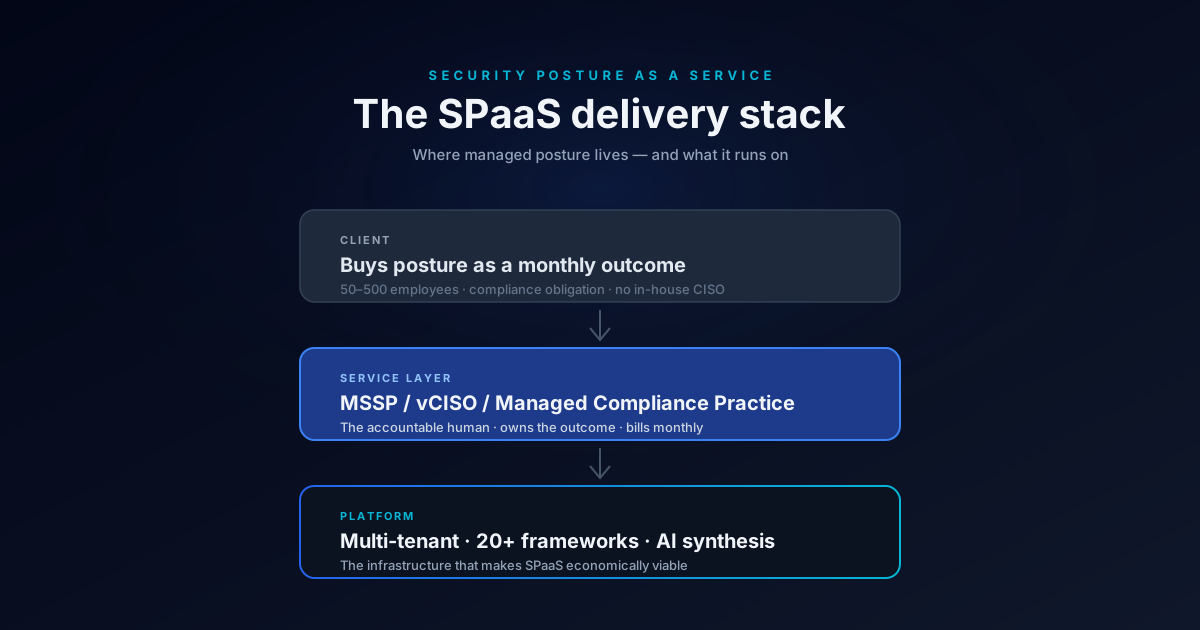
Security Posture as a Service (SPaaS): What It Is, What It Isn't, and Who's Actually Selling It
Security Posture as a Service (SPaaS) defined: the six components every real offering must deliver, who's selling it today, and why the platform decides the economics.
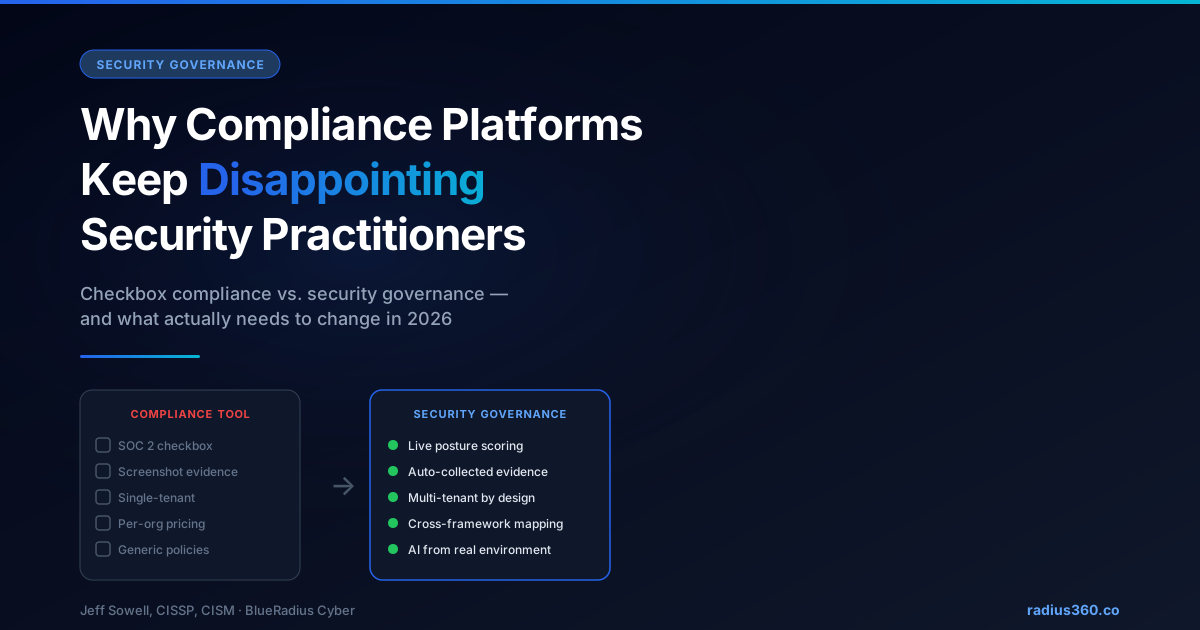
Why Compliance Platforms Keep Disappointing Security Practitioners
Drata and Vanta solved compliance documentation. They didn't solve security governance. Here's why that distinction matters — and what vCISOs, MSSPs, and security leaders actually need from a GRC platform.
OWASP Agentic Top 10: What Every CISO Needs to Know About AI Agent Security
The OWASP Top 10 for Agentic Applications is the first framework purpose-built for autonomous AI security. Here's what each risk means, why it matters, and what to do about it — in plain language.
How to Start a vCISO Practice in 2026: The Complete Guide
A step-by-step guide to launching a fractional CISO practice — from certifications and legal setup to pricing, finding clients, and choosing your tech stack. Based on real practitioner experience.
Building a Mythos-Ready Security Program: What CISOs Need to Do Now
The CSA/SANS 'AI Vulnerability Storm' briefing lays out 13 risks and 11 priority actions. Here's what it means for your GRC practice and how to operationalize it — starting this week.
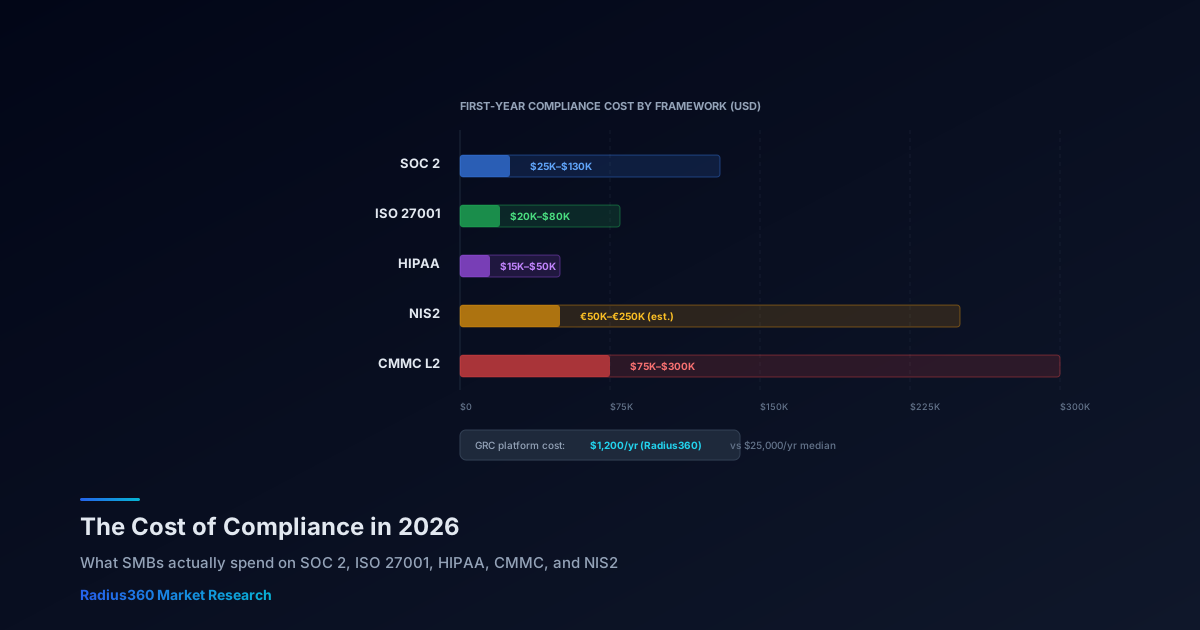
The Cost of Compliance in 2026: What SMBs Actually Spend on SOC 2, ISO 27001, HIPAA, CMMC, and NIS2
Compliance isn't free — but most vendors won't tell you what it actually costs. This data-driven market report breaks down real-world spending on SOC 2, ISO 27001, CMMC, HIPAA, and NIS2 for companies with 20 to 500 employees, with verified cost ranges from audit firms, vendor pricing pages, and industry surveys.
Why Your GRC Platform Should Learn From Every Security Program It Touches
Frameworks tell you what to do. Benchmarks tell you how fast, in what order, and with what priority — based on what actually works across real programs. The next generation of GRC platforms will be defined by their ability to learn.
Ransomware Readiness: The 20-Question Assessment Every CISO Should Run
Ransomware readiness assessment with 20 critical questions mapped to CIS Controls. Evaluate your prevention, detection, response, and recovery posture before attackers do.
CMMC 2.0 Level 2: The Complete Compliance Guide for Defense Contractors
CMMC 2.0 Level 2 compliance guide for defense contractors handling CUI. Covers the 14 NIST 800-171 domains, assessment preparation, and common mistakes to avoid.
How to Price vCISO Services in 2026: Models, Margins, and Mistakes
vCISO pricing models for 2026: hourly, retainer, per-client, and value-based. Learn how to calculate margins, package tiers, and avoid the mistakes that kill profitability.
How to Present Security to the Board: A CISO's Reporting Guide
Board security reporting guide for CISOs: structure a 15-minute briefing, choose metrics that resonate, and answer the three questions every board actually asks.
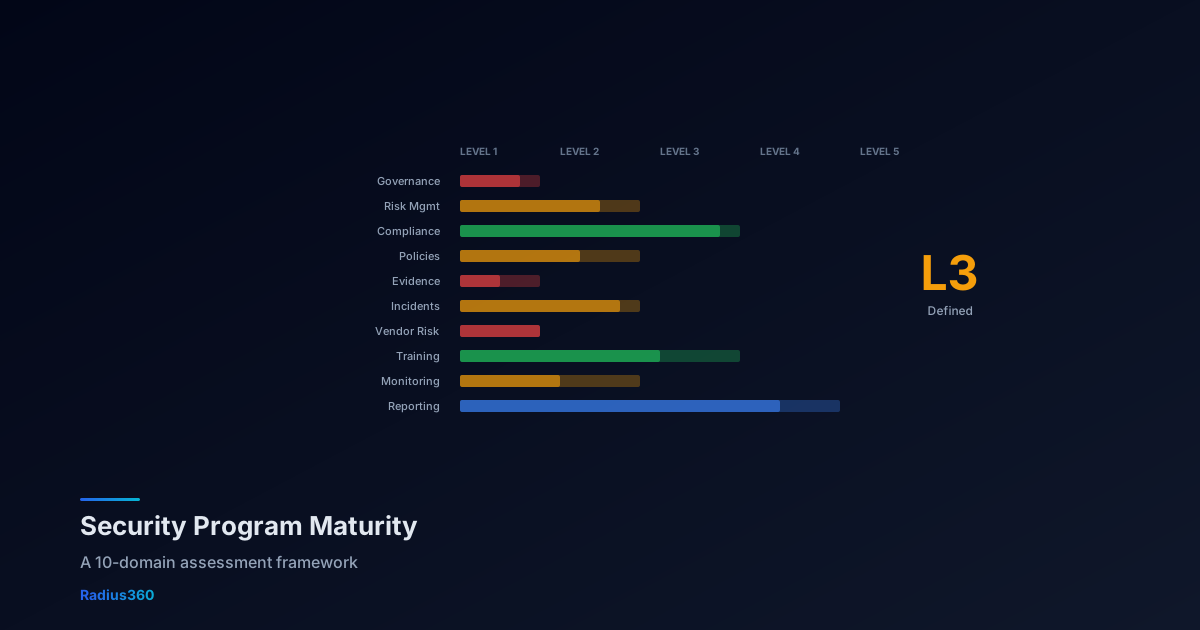
How to Measure Security Program Maturity: A 10-Domain Framework
Most organizations know they need better security, but they can't articulate where they stand today or what 'better' looks like. This 10-domain maturity framework gives you a structured, repeatable way to measure your security program — and a clear path to level up.
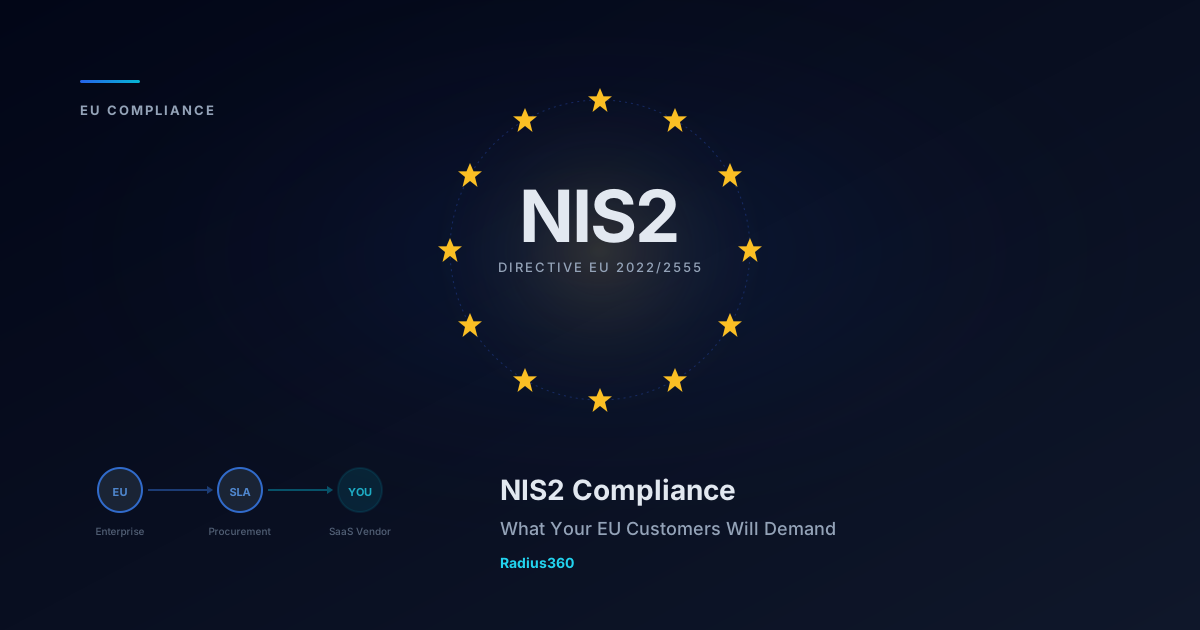
NIS2 Compliance for SaaS Vendors: What Your EU Customers Will Demand
NIS2 compliance deadlines are hitting now. If you sell SaaS to EU enterprises, your customers are about to push their obligations down to you through procurement. Here's what's coming and how to get ready.
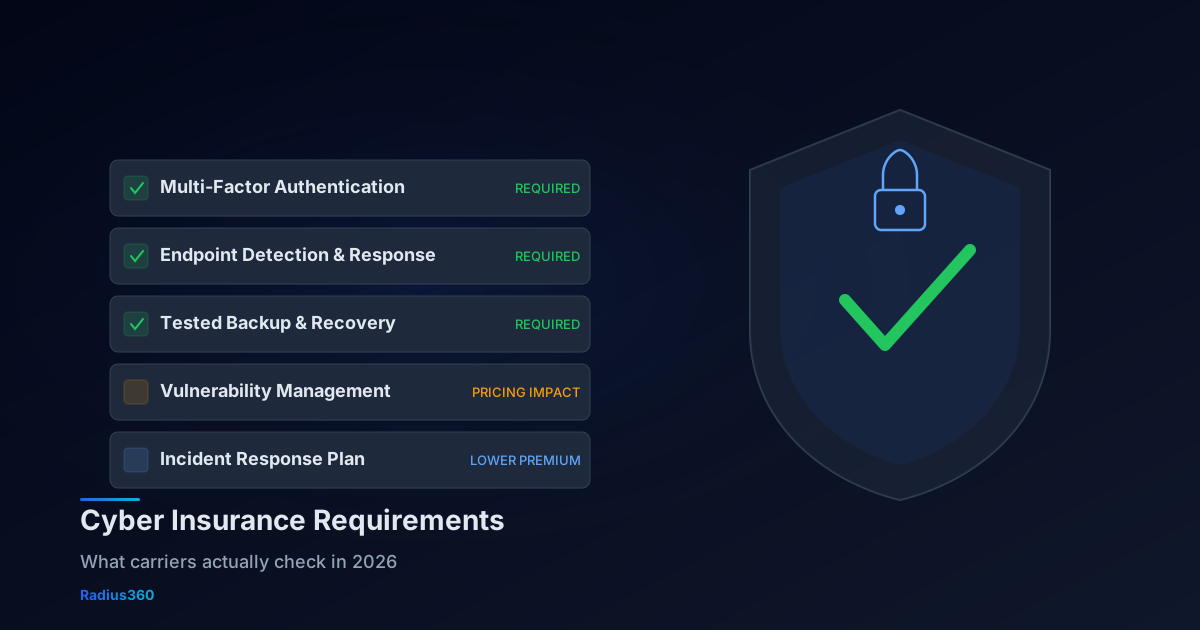
Cyber Insurance Requirements in 2026: What Carriers Actually Check Before They'll Cover You
Cyber insurance applications have become security audits in disguise. Carriers now verify MFA, EDR, backups, and incident response plans before quoting. Here's exactly what they check and how to prove it.
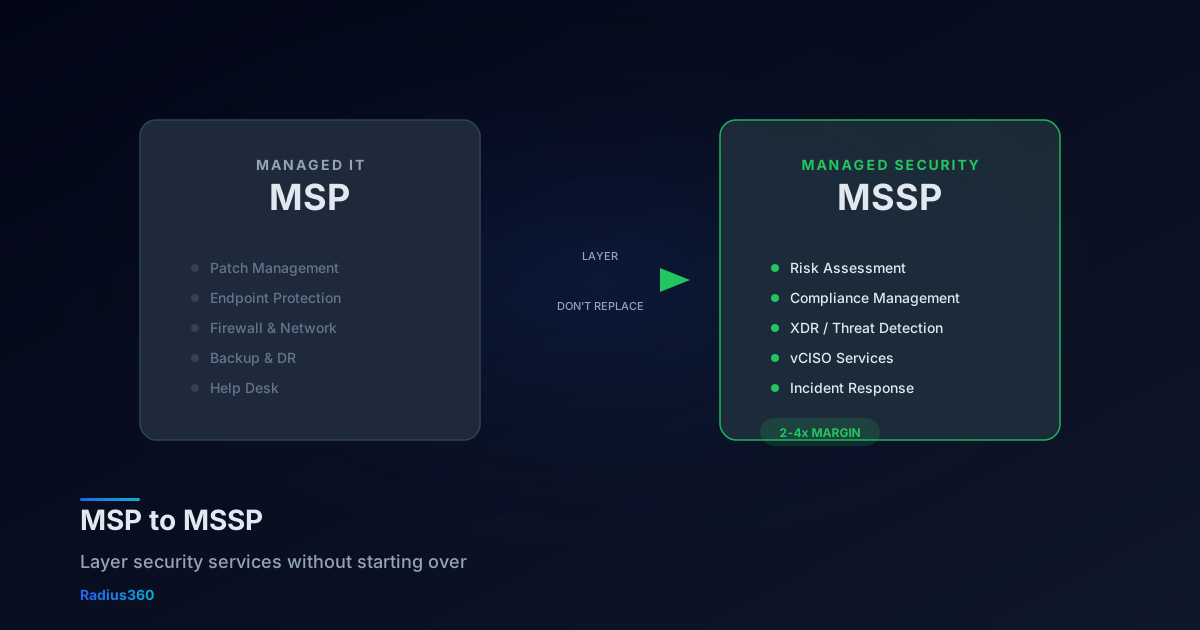
MSP to MSSP: How to Add Security Services Without Starting Over
You don't need to rebuild your business to offer security services. The MSP-to-MSSP transition is about layering capabilities — not replacing what works. Here's how to do it without losing clients or burning out your team.
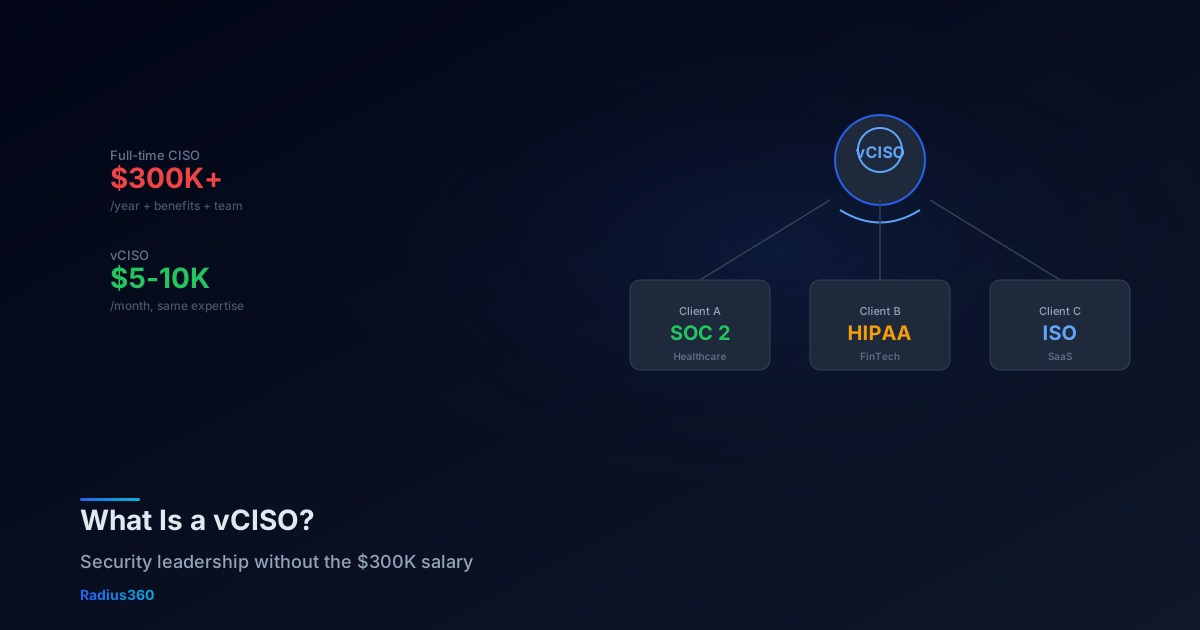
What Is a vCISO? And Does Your Business Actually Need One?
A vCISO gives you executive-level security leadership without the $300K+ salary. Here's what they do, when you need one, and how to find the right fit.
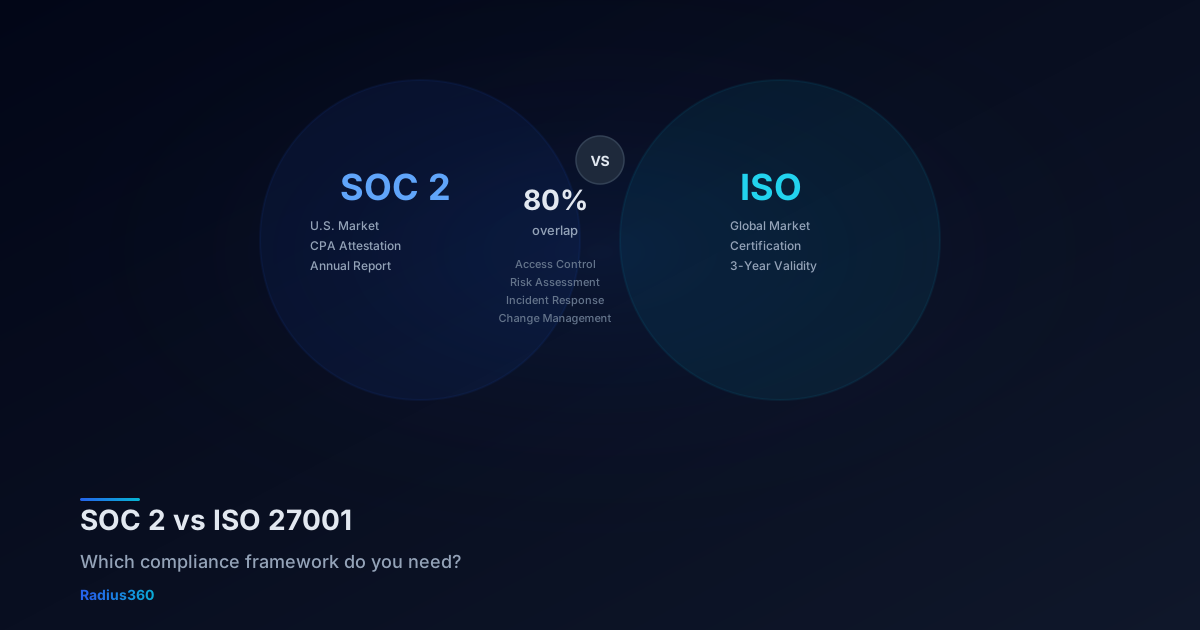
SOC 2 vs ISO 27001: Which Compliance Framework Do You Need?
Both prove you take security seriously, but they serve different audiences. Here's how to decide — and why many companies end up doing both.
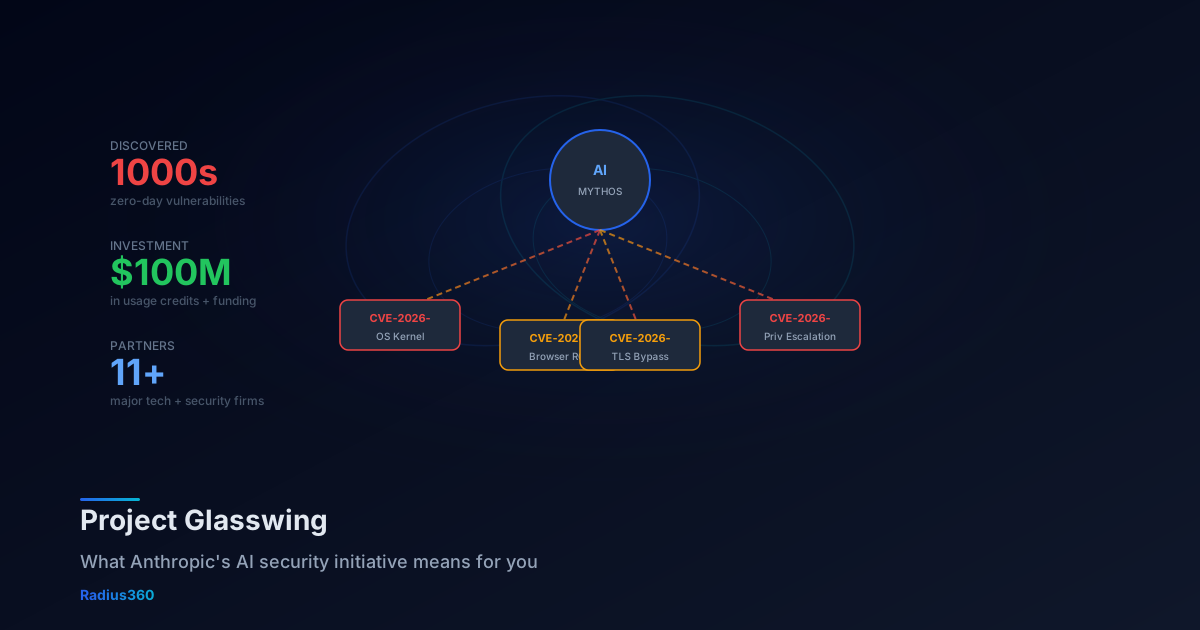
Project Glasswing: What Anthropic's AI Security Initiative Means for Your Security Program
Anthropic's Claude Mythos has discovered thousands of zero-day vulnerabilities in every major OS and browser. A flood of new CVEs is coming. Here's what vCISOs, MSPs, and security leaders need to do now.
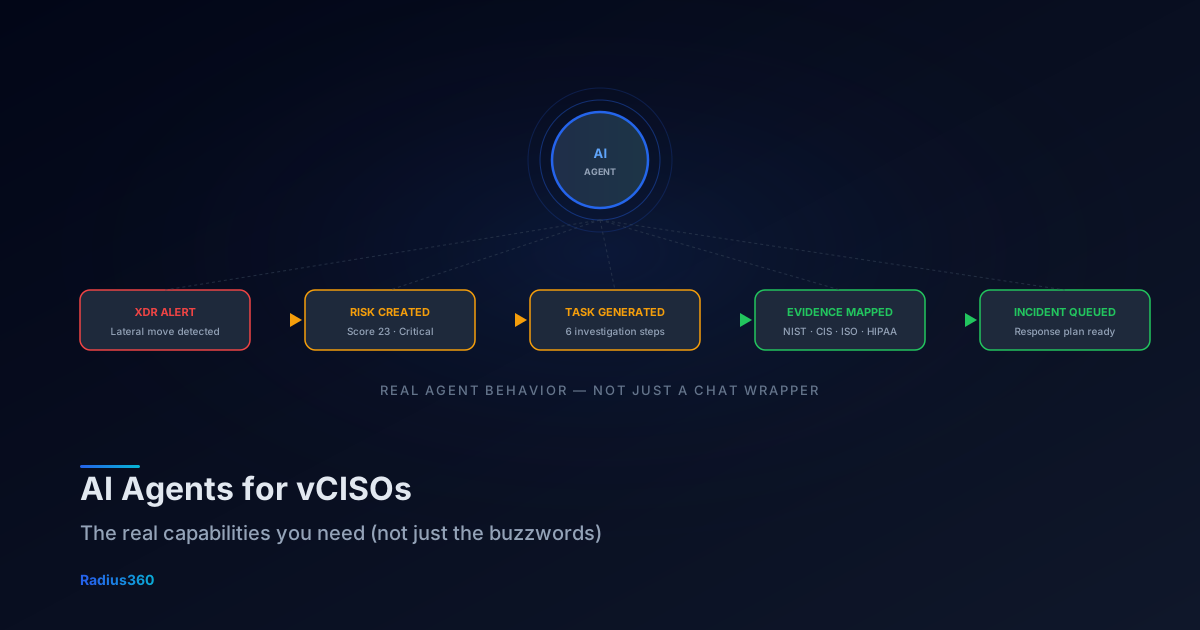
AI Agents for vCISOs: The Real Capabilities You Need (Not Just the Buzzwords)
Every vCISO platform is announcing 'AI agents' this quarter. Here's what actually matters: alert-to-action automation, contextual investigation, and proactive insights that fix things — not just describe them.
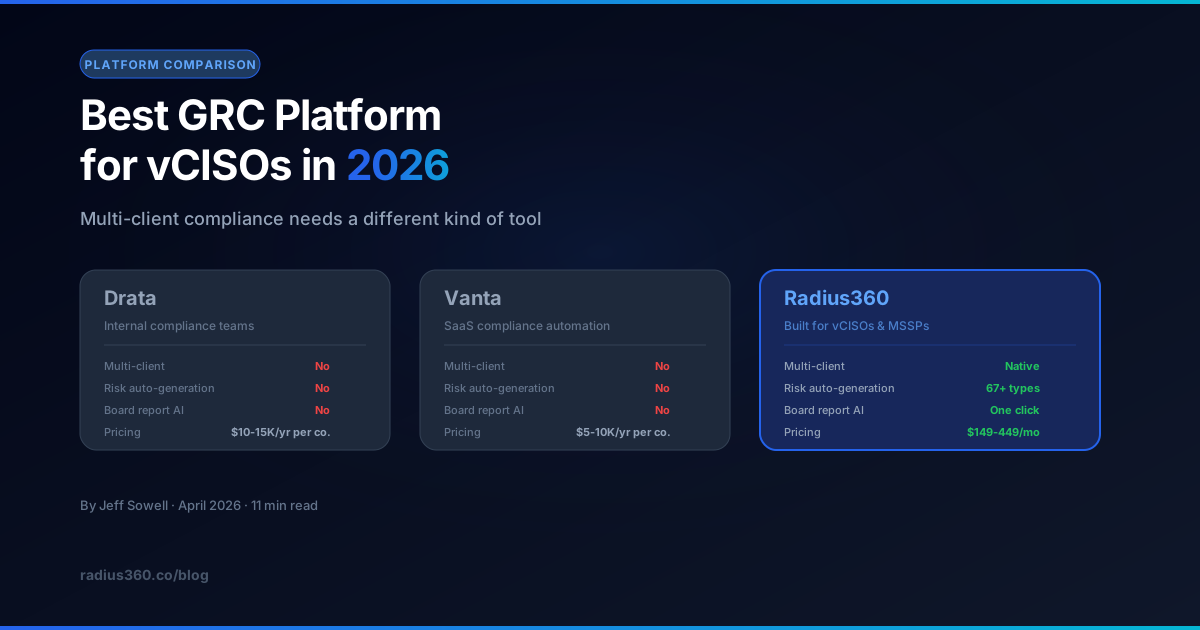
Best GRC Platform for vCISOs in 2026: Drata vs. Vanta vs. Radius360
Drata and Vanta are built for internal compliance teams. If you're a vCISO or MSSP managing multiple clients, you need a platform built for practitioners — not a tool designed for a single company's audit.
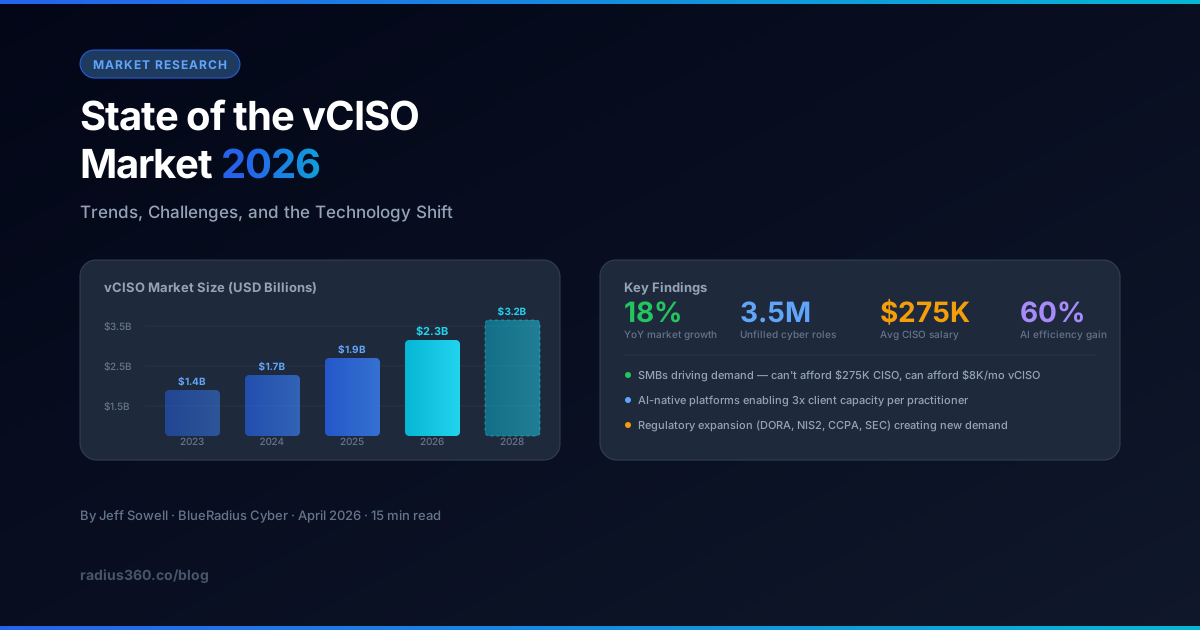
State of the vCISO Market 2026: Trends, Challenges, and the Technology Shift
The vCISO market is projected to reach $3.2B by 2027, driven by regulatory expansion, the CISO talent gap, and AI-native platforms that let one practitioner do the work of three. Here's what the data says — and what it means for your practice.
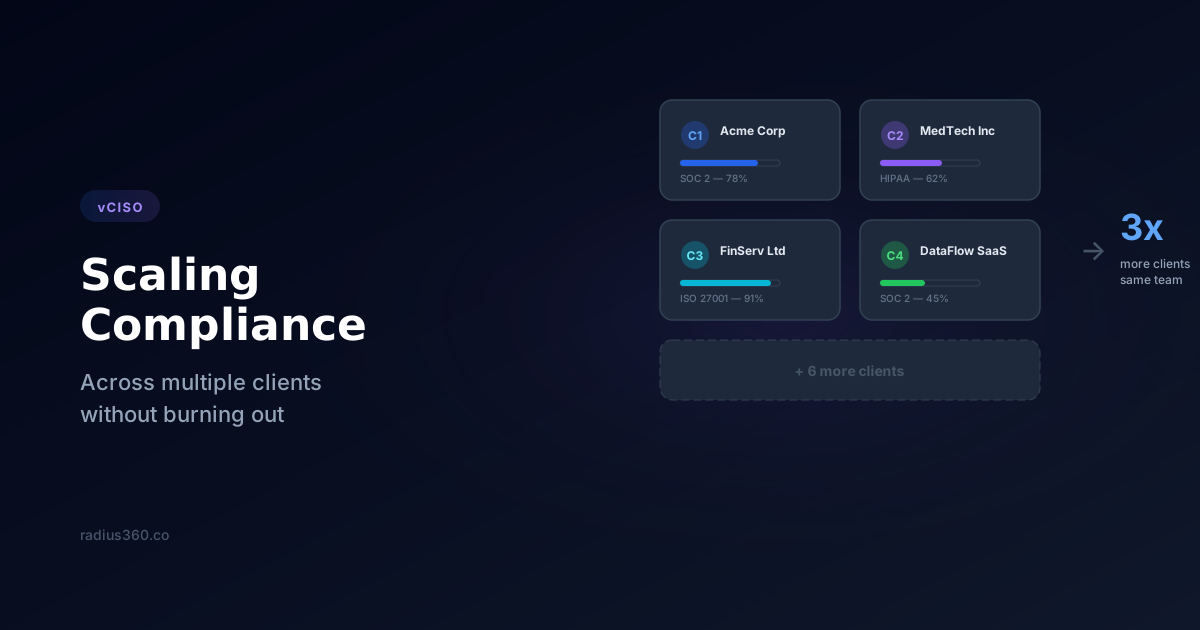
How vCISOs Can Scale Compliance Across Multiple Clients
Managing compliance for one company is hard enough. Here's how virtual CISOs can scale their practice across 5, 10, or 20 clients without burning out or dropping balls.
NIST CSF 2.0: What Changed and How to Implement It
NIST CSF 2.0 introduced a sixth function — Govern — and restructured the entire framework. Here's what changed, why it matters, and a practical roadmap for implementing it in your organization.
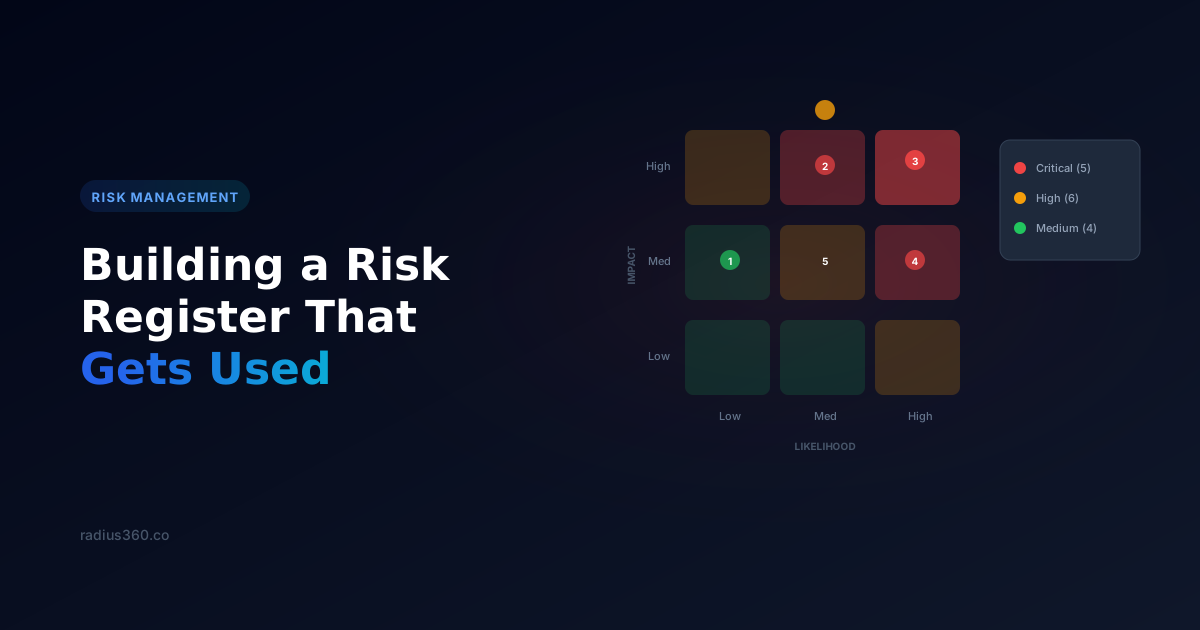
How to Build a Risk Register That Actually Gets Used
Most risk registers are graveyards of outdated spreadsheets. Here's how to build one that stays current, drives decisions, and doesn't make your team's eyes glaze over.
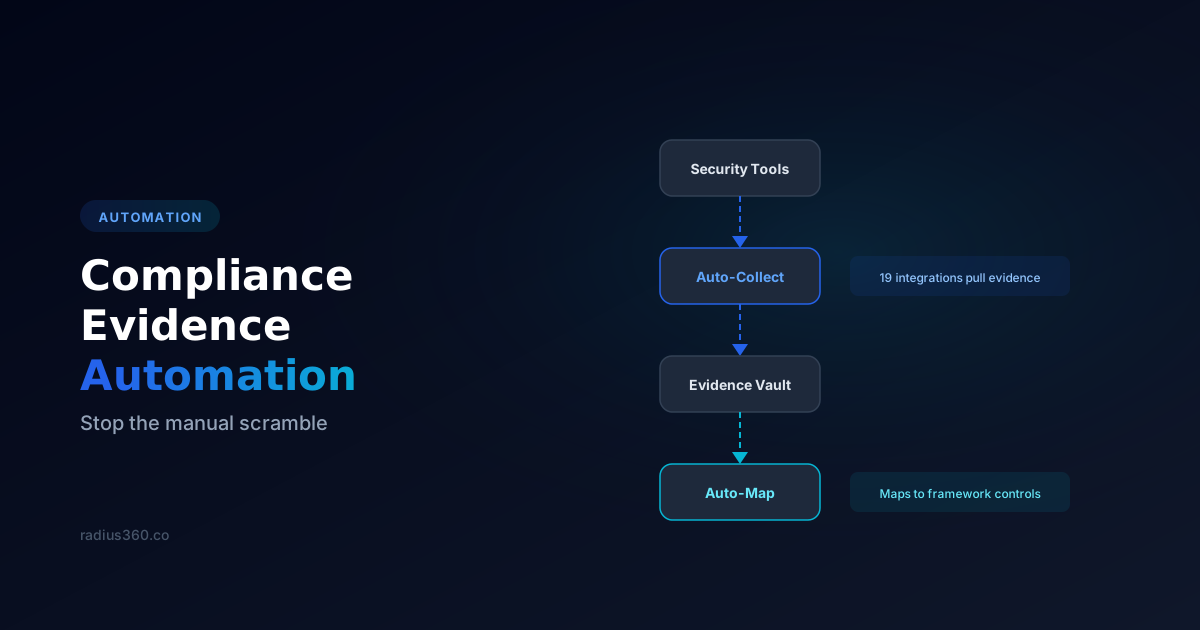
How to Automate Compliance Evidence Collection (And Stop the Audit Scramble)
Manual evidence collection doesn't scale. Here's how to build an automated evidence pipeline that keeps your compliance program audit-ready year-round, not just the week before.
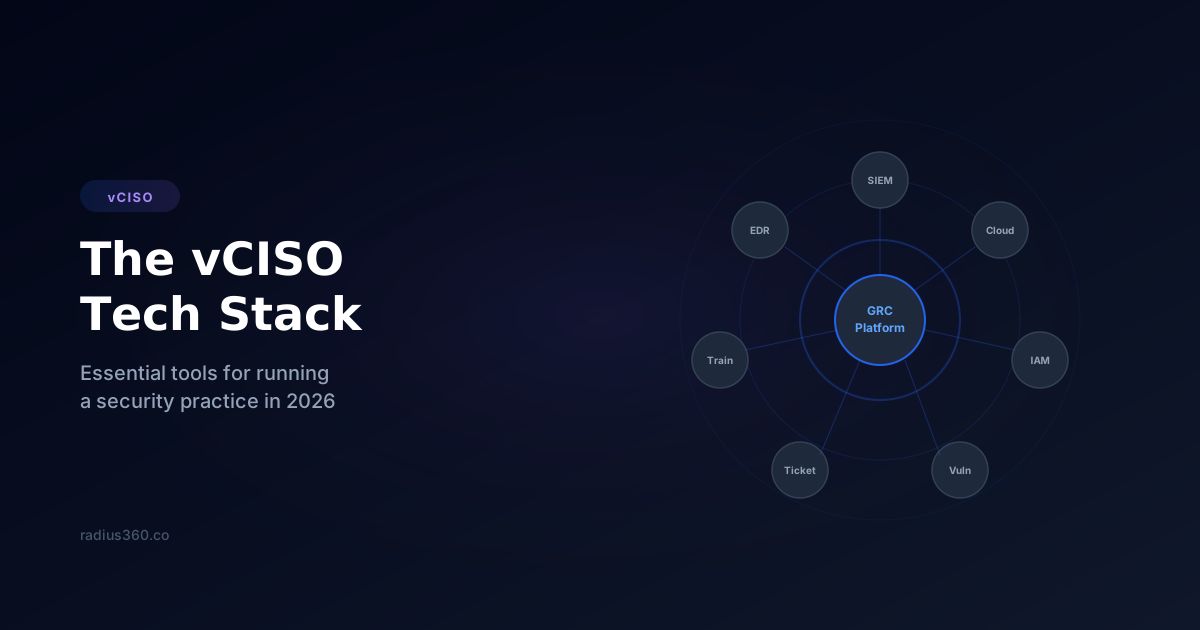
The vCISO's Tech Stack: Essential Tools for Running a Security Practice in 2026
The right tools turn a solo vCISO into a scalable practice. Here's the definitive tech stack for managing multiple clients, delivering professional output, and reclaiming your weekends.
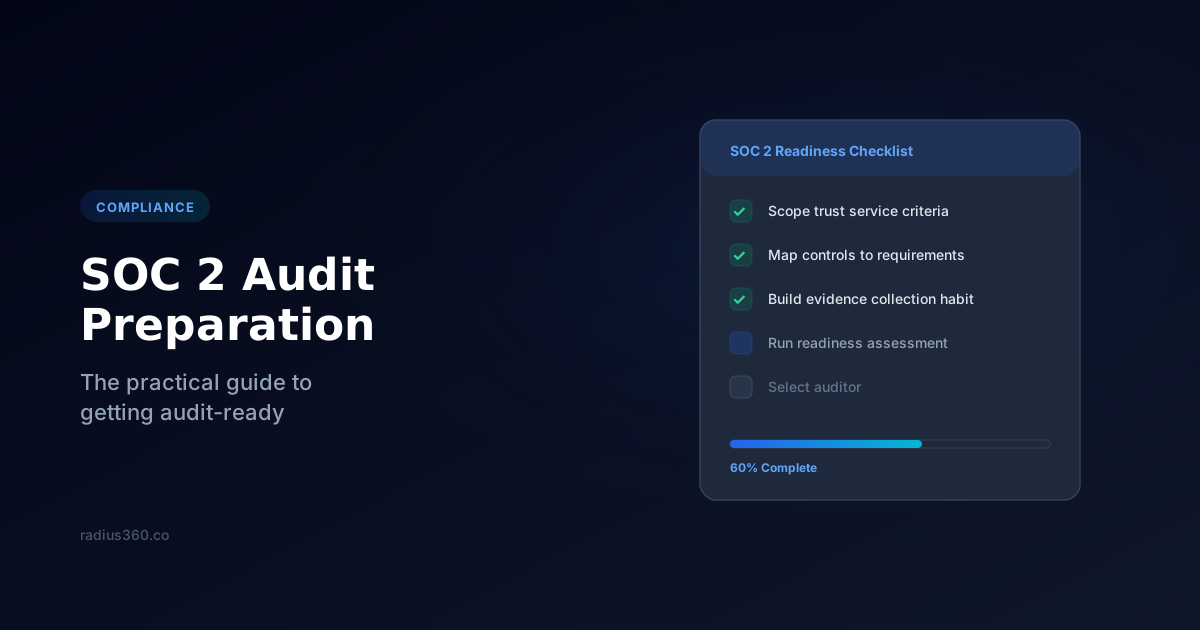
How to Prepare for a SOC 2 Audit Without Losing Your Mind
SOC 2 doesn't have to be a fire drill. Here's a practical guide to getting audit-ready — from scoping your trust service criteria to collecting evidence that actually holds up.
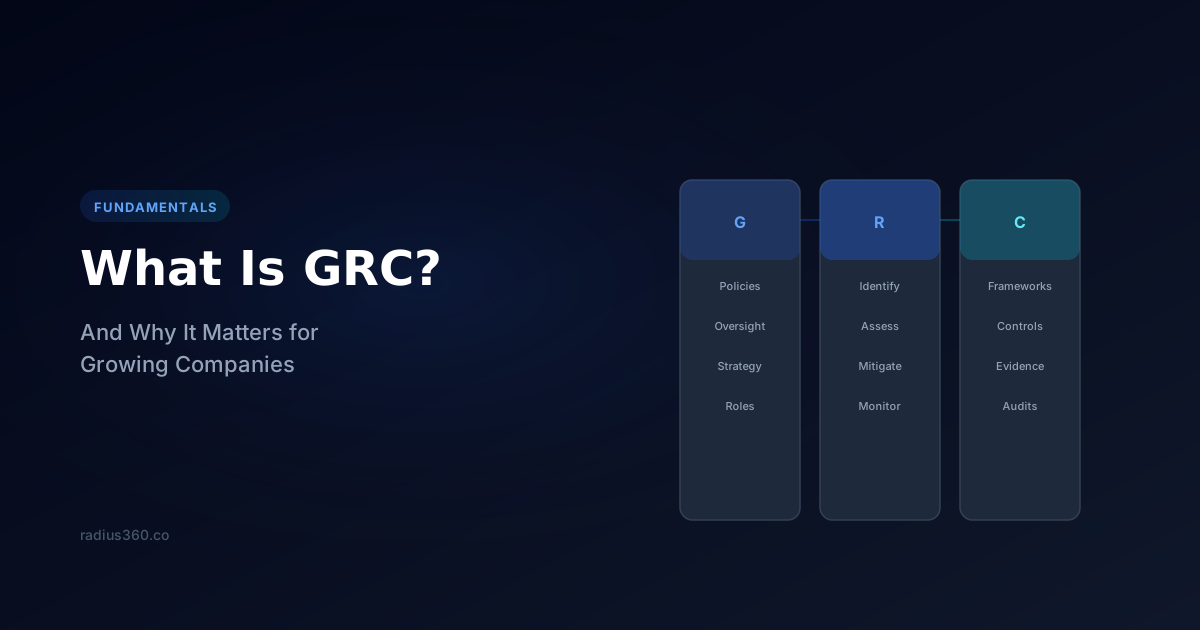
What Is GRC and Why Does It Matter for Growing Companies?
Governance, risk, and compliance isn't just for enterprises. If your company handles sensitive data, works with regulated clients, or wants to close bigger deals — GRC is how you prove you're ready.

We use cookies
We use strictly necessary cookies to make Radius360 work. With your consent, we'd also like to use analytics cookies to understand how visitors use our site so we can improve it. You can change your choice anytime. See our Privacy Policy.