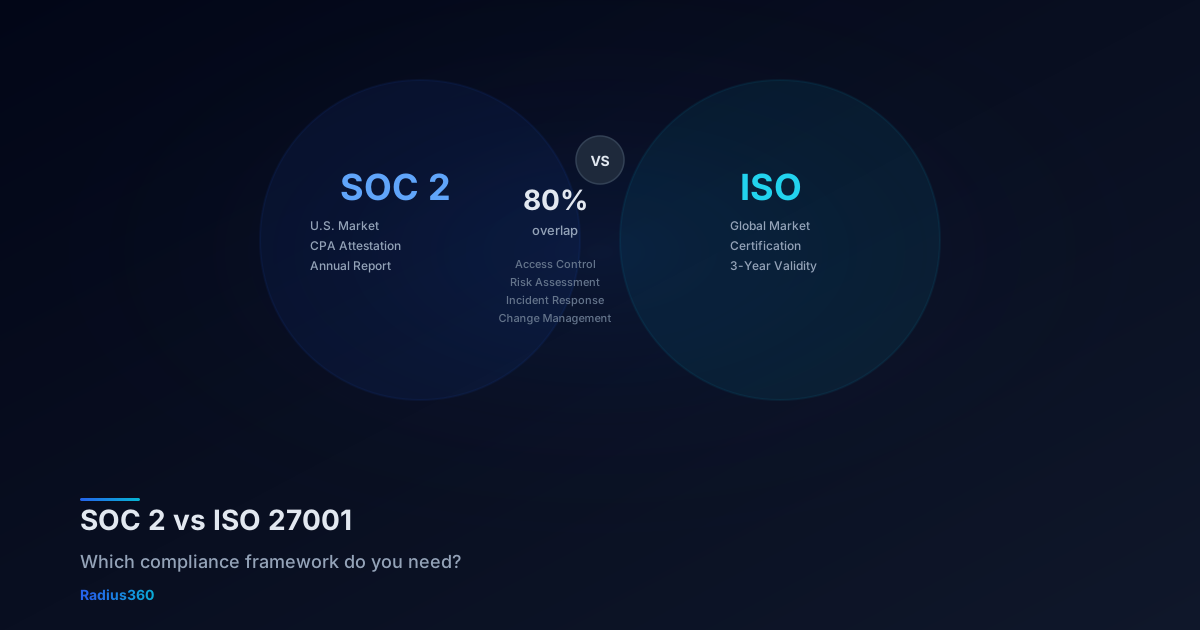
Two frameworks, one question
If you're a growing SaaS company, a service provider, or any business that handles customer data, you've probably been asked: "Do you have SOC 2?" or "Are you ISO 27001 certified?" Sometimes both in the same week.
Both frameworks prove that your organization manages security effectively. But they come from different worlds, serve different audiences, and work differently. Choosing the right one (or both) depends on your customers, your market, and your growth plans.
SOC 2: The American standard
What it is: An auditing framework developed by the AICPA (American Institute of Certified Public Accountants). A SOC 2 report is issued by a licensed CPA firm after auditing your controls against the Trust Services Criteria.
Who asks for it: Primarily U.S. companies. If your customers are American enterprises, they'll ask for SOC 2. It's the de facto standard for SaaS vendors, cloud providers, and technology services in North America.
How it works:
- Type I: Auditor evaluates your control design at a point in time
- Type II: Auditor tests that controls operated effectively over 3-12 months
- Report is issued by the auditor to you; you share it with customers under NDA
- Not a certification — it's an attestation report with the auditor's opinion
Trust Services Criteria (pick what applies):
- Security (required): The common criteria — access controls, monitoring, incident response
- Availability: Uptime, disaster recovery, performance monitoring
- Processing Integrity: Data processing accuracy and completeness
- Confidentiality: Data protection and access restrictions
- Privacy: Personal information handling per privacy commitments
Timeline: 3-6 months to prepare, then 3-12 month observation period for Type II.
Cost: $15,000-$50,000 for the audit, plus preparation costs. A GRC platform significantly reduces prep time.
For a detailed preparation guide, see our SOC 2 Audit Preparation Guide.
ISO 27001: The global standard
What it is: An international standard published by ISO/IEC for information security management systems (ISMS). Certification is issued by an accredited certification body after a formal audit.
Who asks for it: International companies, European enterprises, government agencies, and organizations in regulated industries globally. If you sell outside North America, ISO 27001 is often required.
How it works:
- Stage 1 audit: Certification body reviews your ISMS documentation
- Stage 2 audit: On-site (or remote) audit verifying controls are implemented and effective
- Certification is valid for 3 years with annual surveillance audits
- It IS a certification — you can say "ISO 27001 certified" and use the badge
Structure:
- Clauses 4-10: Management system requirements (context, leadership, planning, support, operation, performance evaluation, improvement)
- Annex A: 93 controls across 4 themes (organizational, people, physical, technological)
- You must produce a Statement of Applicability (SoA) documenting which controls apply and why
Timeline: 6-12 months to implement the ISMS, then 2-4 weeks for the certification audit.
Cost: $20,000-$80,000+ depending on company size and complexity. Certification audit itself is $10,000-$30,000.
Head-to-head comparison
| Dimension | SOC 2 | ISO 27001 |
|---|---|---|
| Origin | U.S. (AICPA) | International (ISO/IEC) |
| Type | Attestation report | Certification |
| Audience | North American enterprises | Global market |
| Auditor | Licensed CPA firm | Accredited certification body |
| Scope | You choose TSC categories | Full ISMS with Annex A controls |
| Duration | Report valid 12 months | Certificate valid 3 years |
| Renewal | New audit annually | Surveillance audits + recertification at year 3 |
| Approach | Control-focused (prove controls work) | System-focused (prove ISMS is effective) |
| Flexibility | Choose applicable criteria | Must address all Annex A controls (with justification for exclusions) |
| Public claim | "We completed a SOC 2 Type II audit" | "We are ISO 27001 certified" |
How to decide
Go with SOC 2 if:
- Your customers are primarily in North America
- Prospects are asking specifically for SOC 2 reports
- You need the fastest path to a credible security attestation
- You're a SaaS company, cloud provider, or technology services firm
Go with ISO 27001 if:
- You sell internationally, especially in Europe
- Your customers or partners require ISO certification specifically
- You want a longer-lived credential (3-year cert vs. annual report)
- You're in a regulated industry that references ISO standards
Do both if:
- You sell to both U.S. and international customers
- Enterprise prospects have varying requirements
- You want maximum credibility in competitive deals
- You're building a long-term security program (the overlap makes dual compliance efficient)
The 80% overlap
Here's the good news: SOC 2 and ISO 27001 overlap significantly. If you've done one, you're most of the way to the other.
| Control Area | SOC 2 | ISO 27001 |
|---|---|---|
| Access control | CC6.1-6.8 | A.9 |
| Incident response | CC7.3-7.5 | A.16 |
| Change management | CC8.1 | A.12.1, A.14.2 |
| Risk assessment | CC3.1-3.4 | 6.1, A.8 |
| Vendor management | CC9.2 | A.15 |
| Security awareness | CC1.4 | A.7.2.2 |
| Encryption | CC6.1, CC6.7 | A.10 |
| Monitoring & logging | CC7.1-7.2 | A.12.4 |
| Business continuity | A1.1-A1.3 | A.17 |
With a GRC platform that supports cross-framework mapping, a control you assess for SOC 2 automatically maps to the corresponding ISO 27001 control. You do the work once and satisfy both frameworks.
Common mistakes
Starting without a risk assessment. Both frameworks require one. Do it first — it drives everything else. See our guide on building a risk register.
Treating compliance as a project, not a program. SOC 2 Type II requires sustained compliance over a review period. ISO 27001 requires continuous improvement. Both fail if you cram before the audit.
Manual evidence collection. The biggest time sink in either audit is gathering evidence. Automated evidence collection from your existing tools (identity provider, cloud platform, SIEM, EDR) cuts this from weeks to hours.
Going it alone. A vCISO or compliance consultant can save months of trial and error. BlueRadius guides organizations through both SOC 2 and ISO 27001 implementation — from initial gap assessment through successful audit.
Bottom line
SOC 2 and ISO 27001 aren't competing — they're complementary. SOC 2 is your ticket to the U.S. enterprise market. ISO 27001 is your ticket to the global market. Most growing companies will eventually need both.
Start with whichever your customers are asking for. Build the security program once, map it to both frameworks, and let the overlap work in your favor.
Need help deciding? BlueRadius helps organizations choose and implement the right compliance frameworks. Start with a free compliance assessment or explore Radius360 to manage both frameworks from one platform.
